SSO in Pachca with Authentik
This setup lets employees log in to Pachca using goauthentik.io
Setting up OpenID SSO in a running Authentik container.
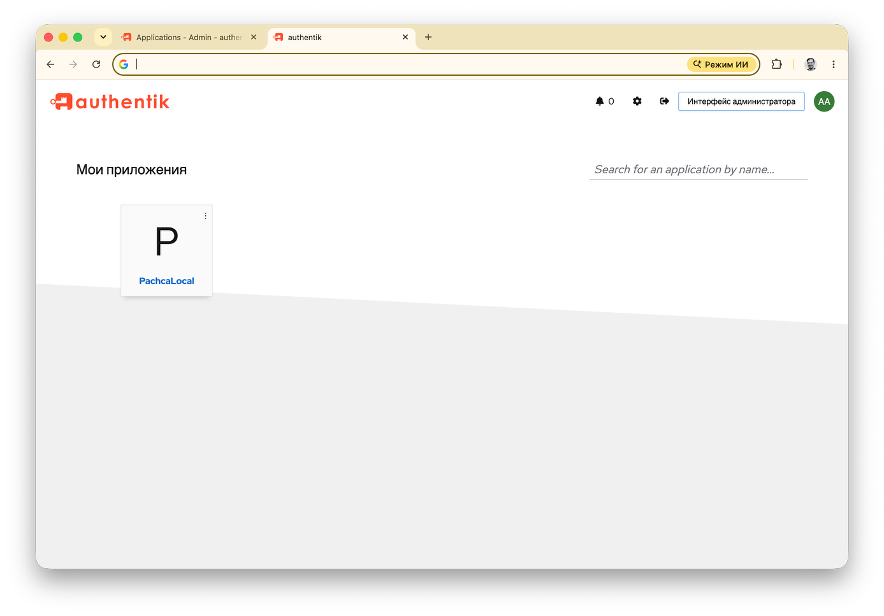
Go to the Admin interface.
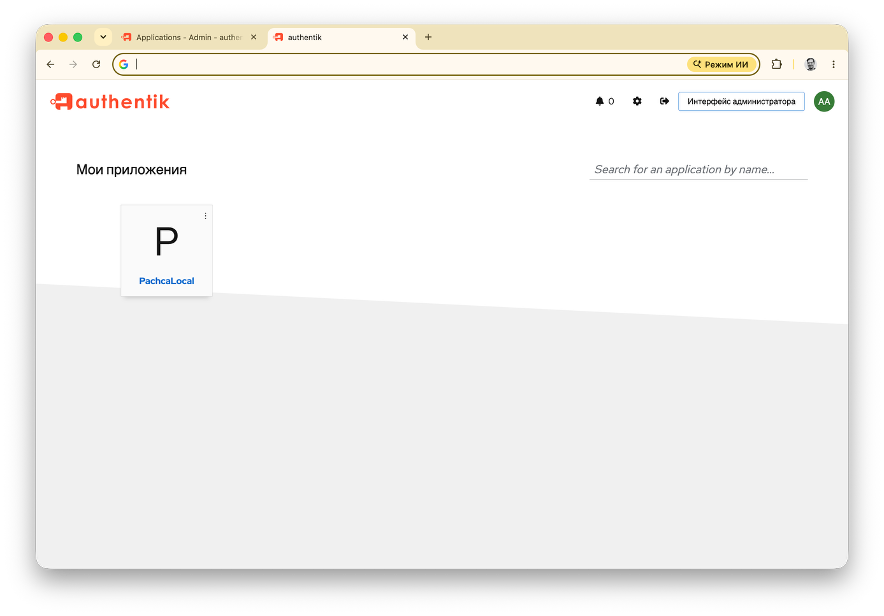
Go to Applications and click Create with provider.
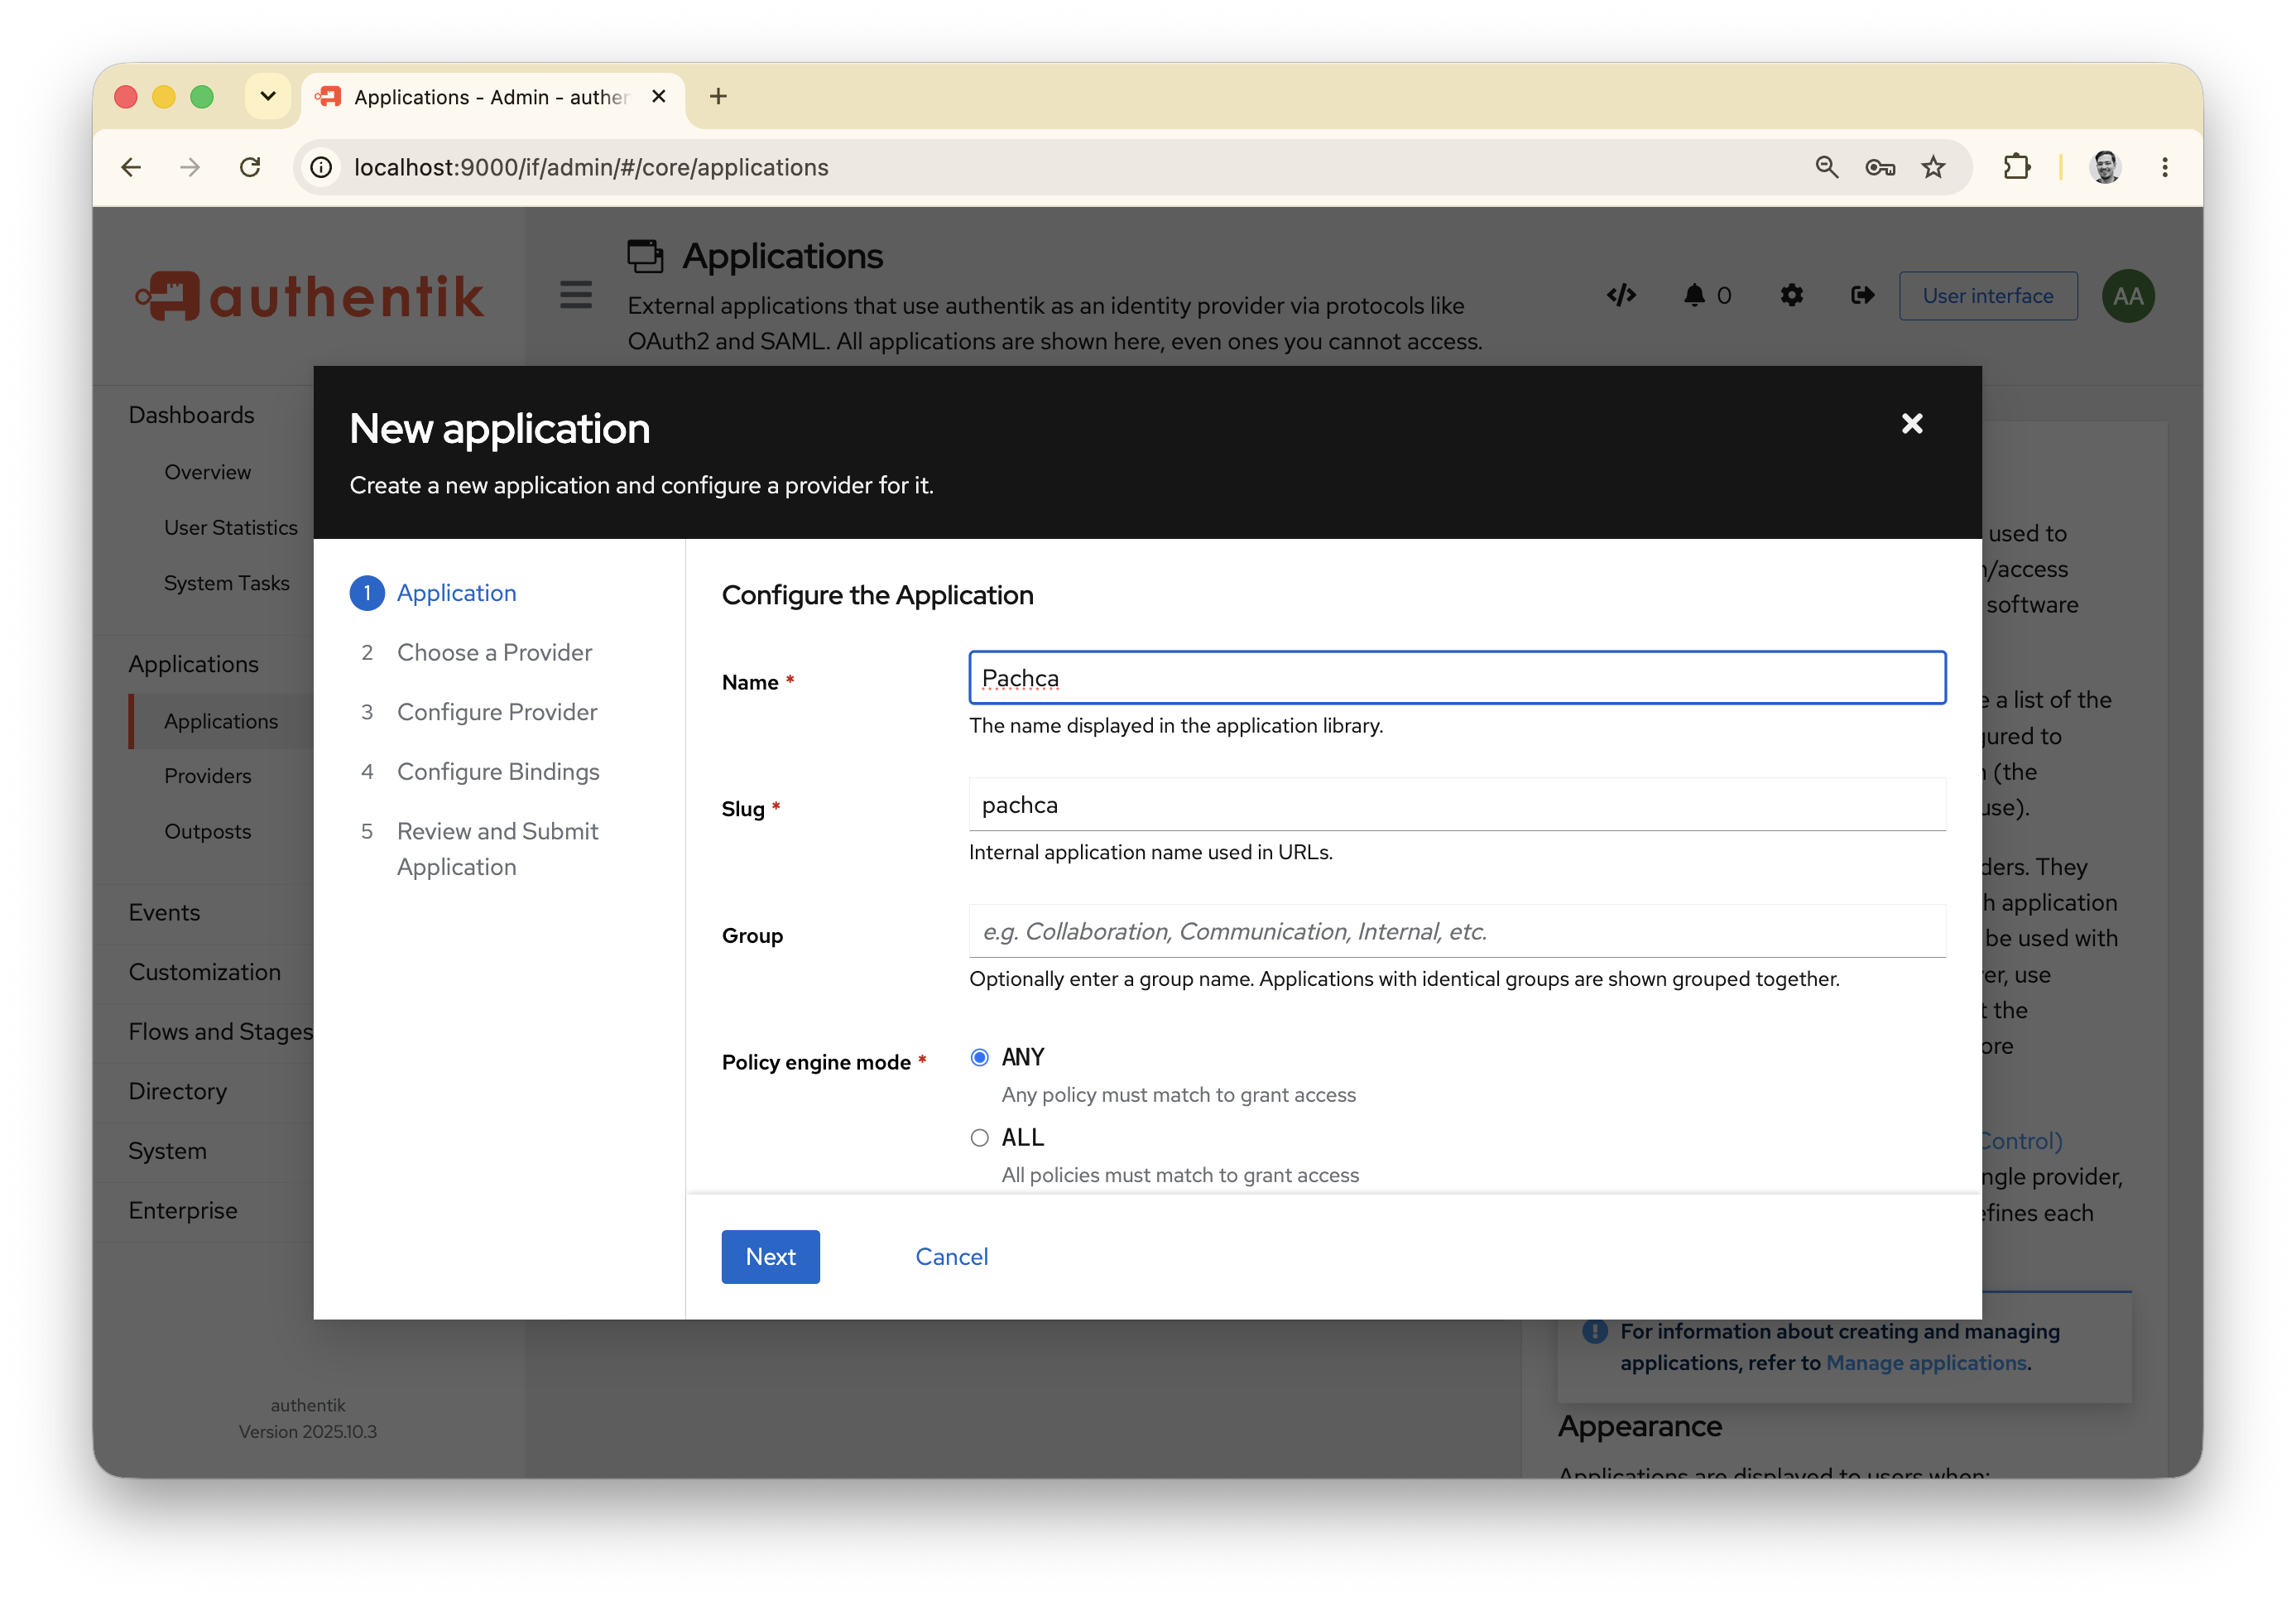
Enter any name and click Next.
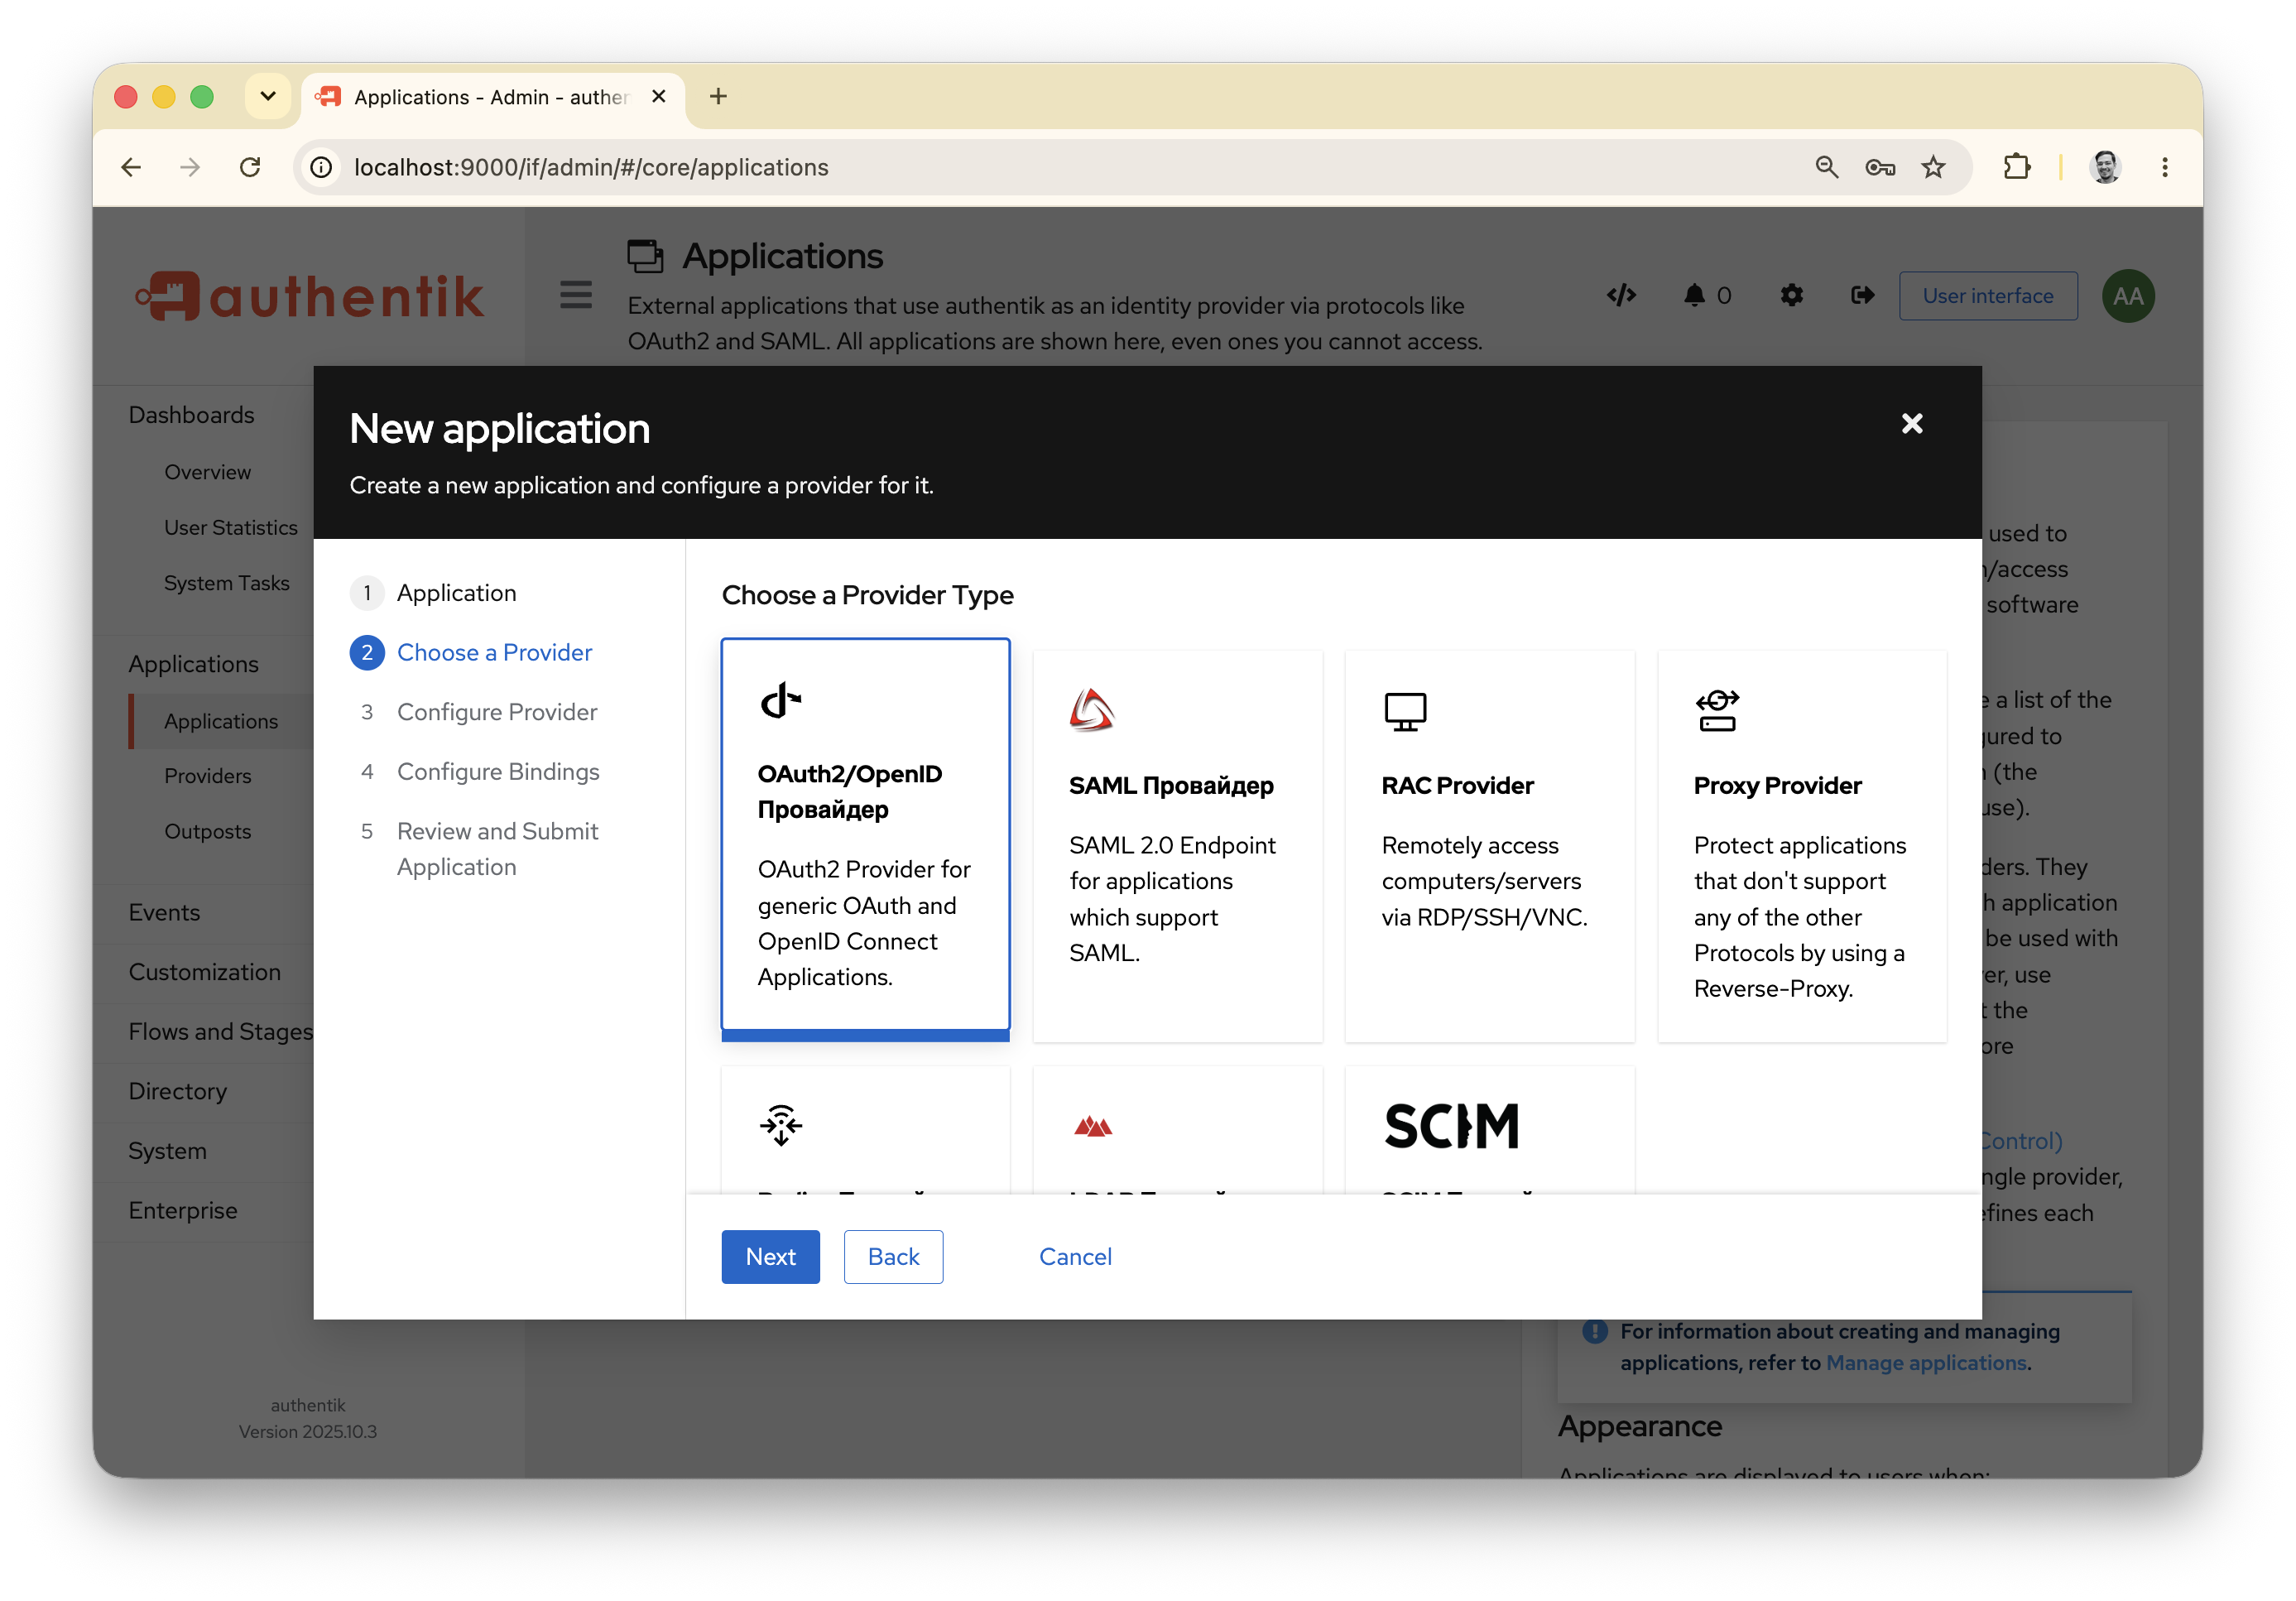
Select the OAuth2/OpenID provider and click Next.
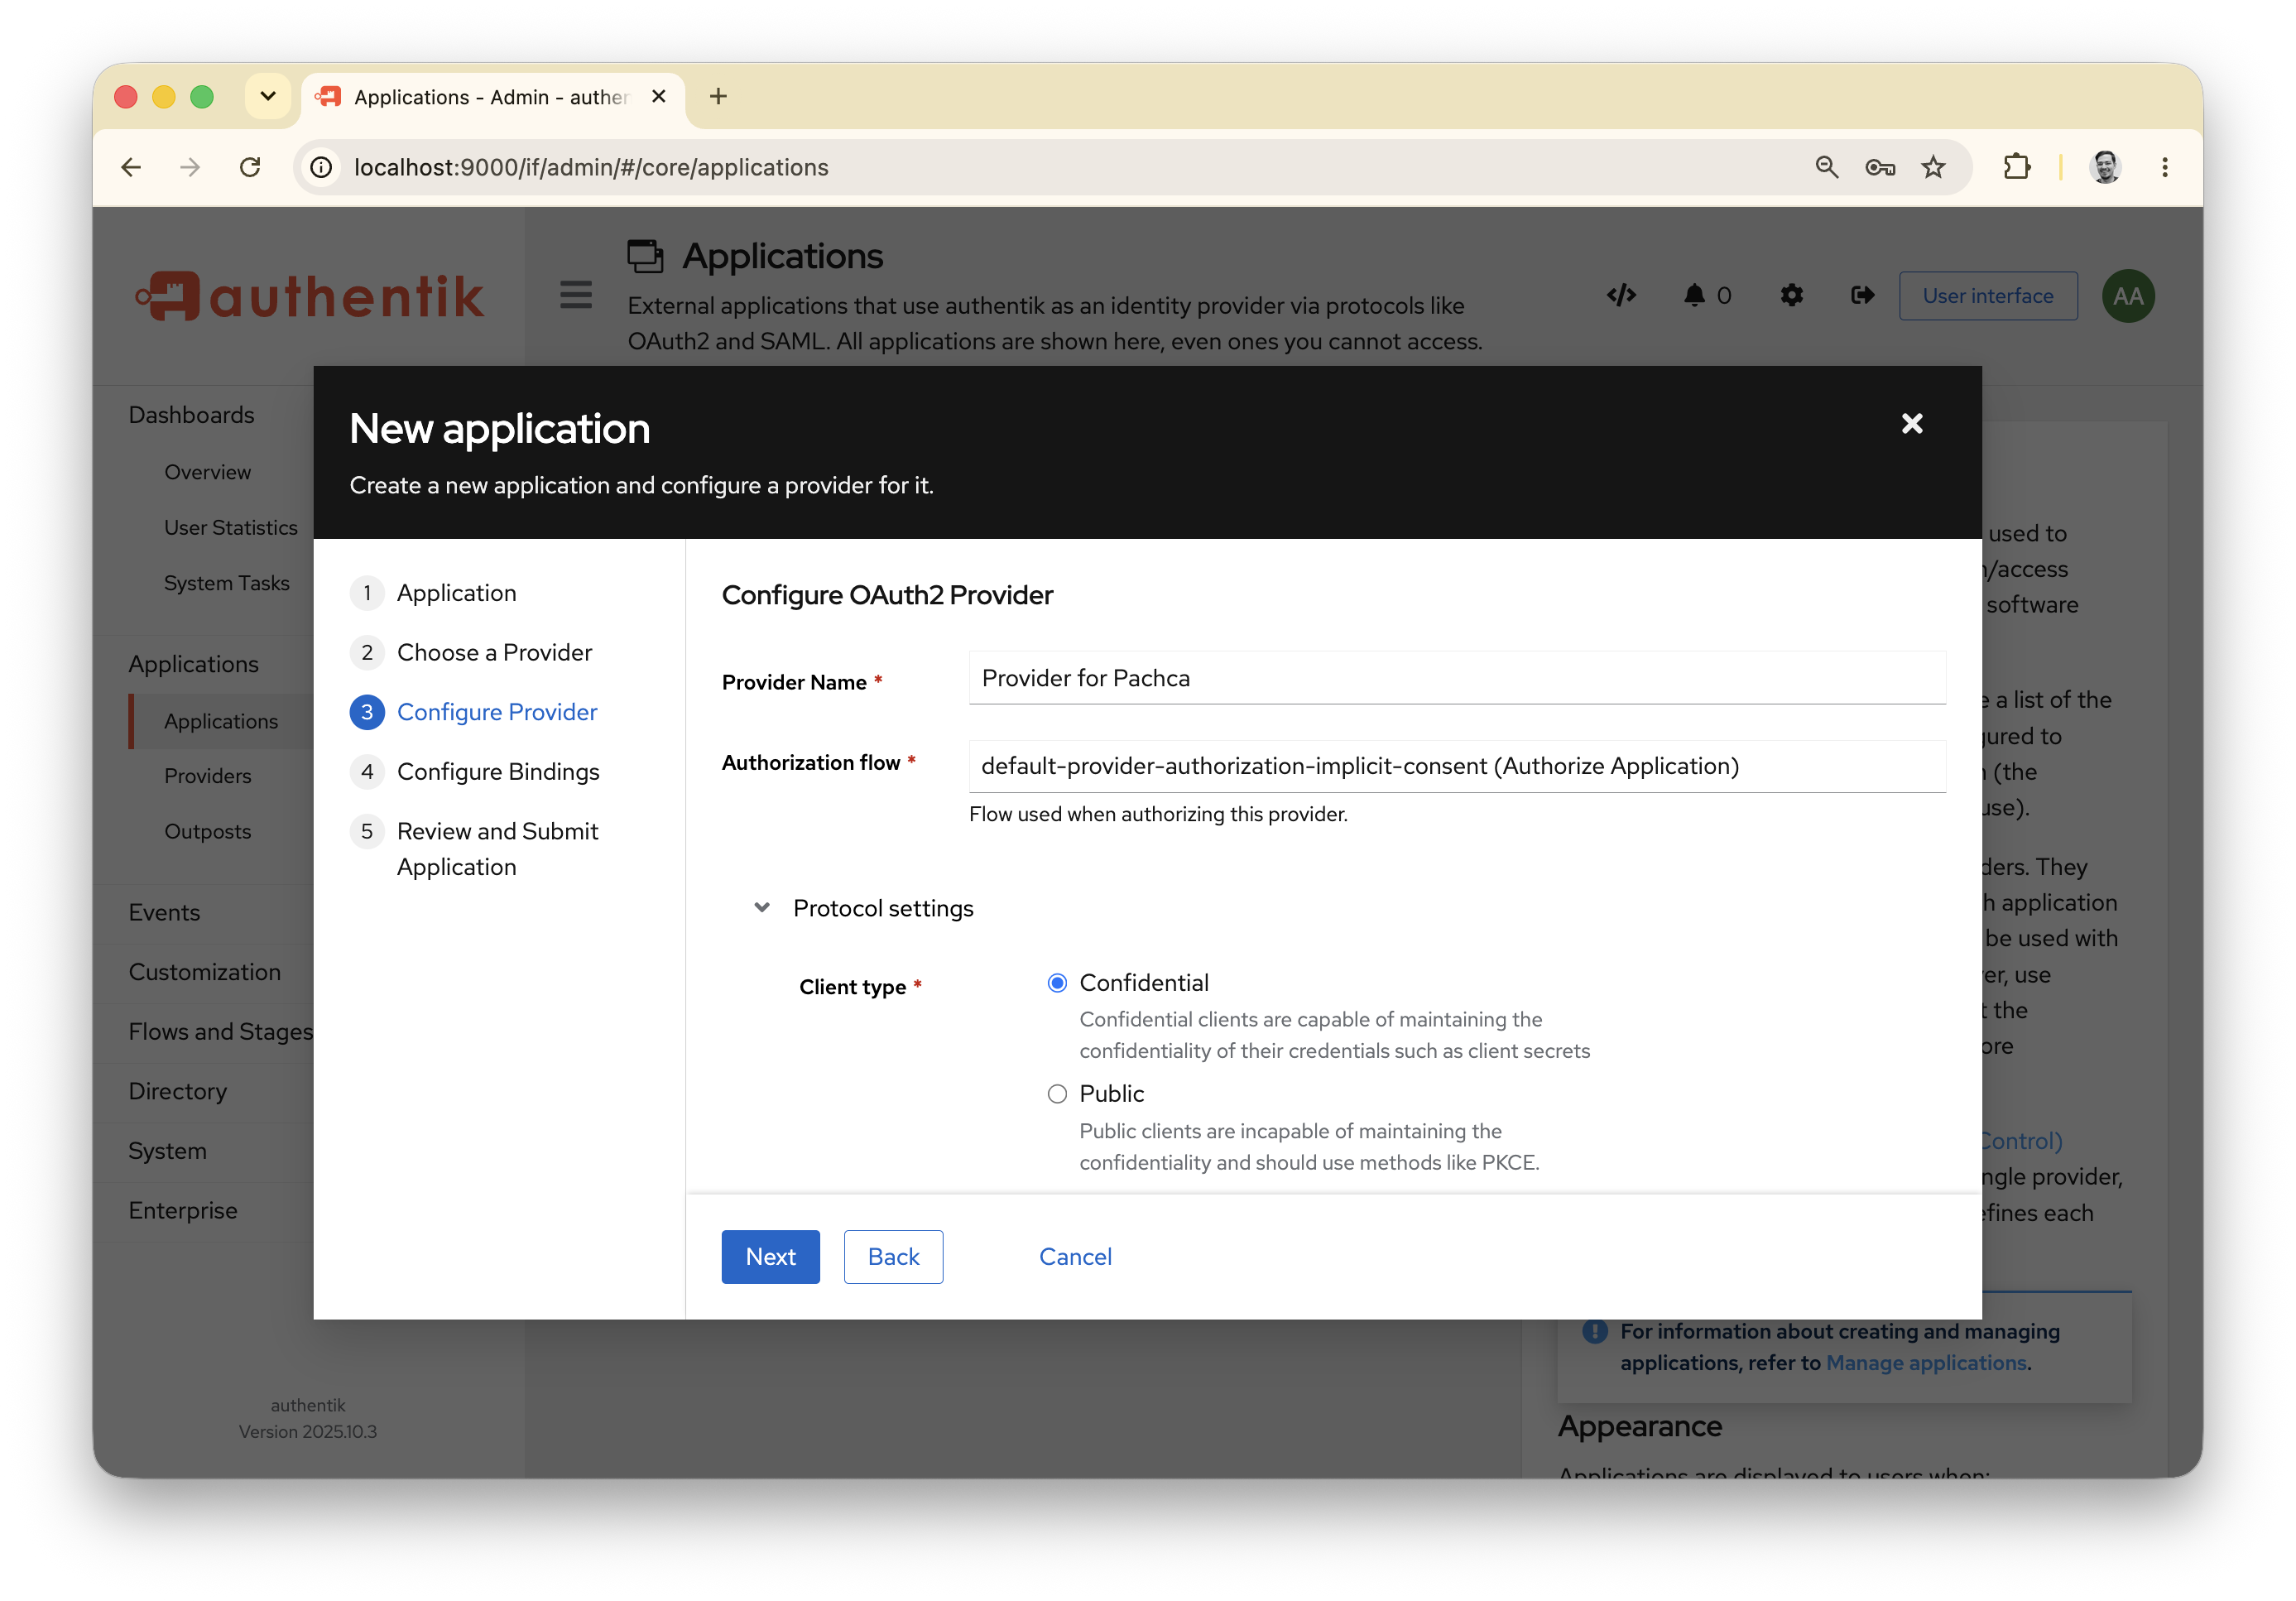
In this form, set: Authorization flow: default-provider-authorization-implicit-consent Client type: confidential Redirect URIs: the URL we'll send you. Copy the Client ID and Client Secret and send them to us.
Click Next and Submit.
Go to Providers and send us the OpenID Configuration URL.
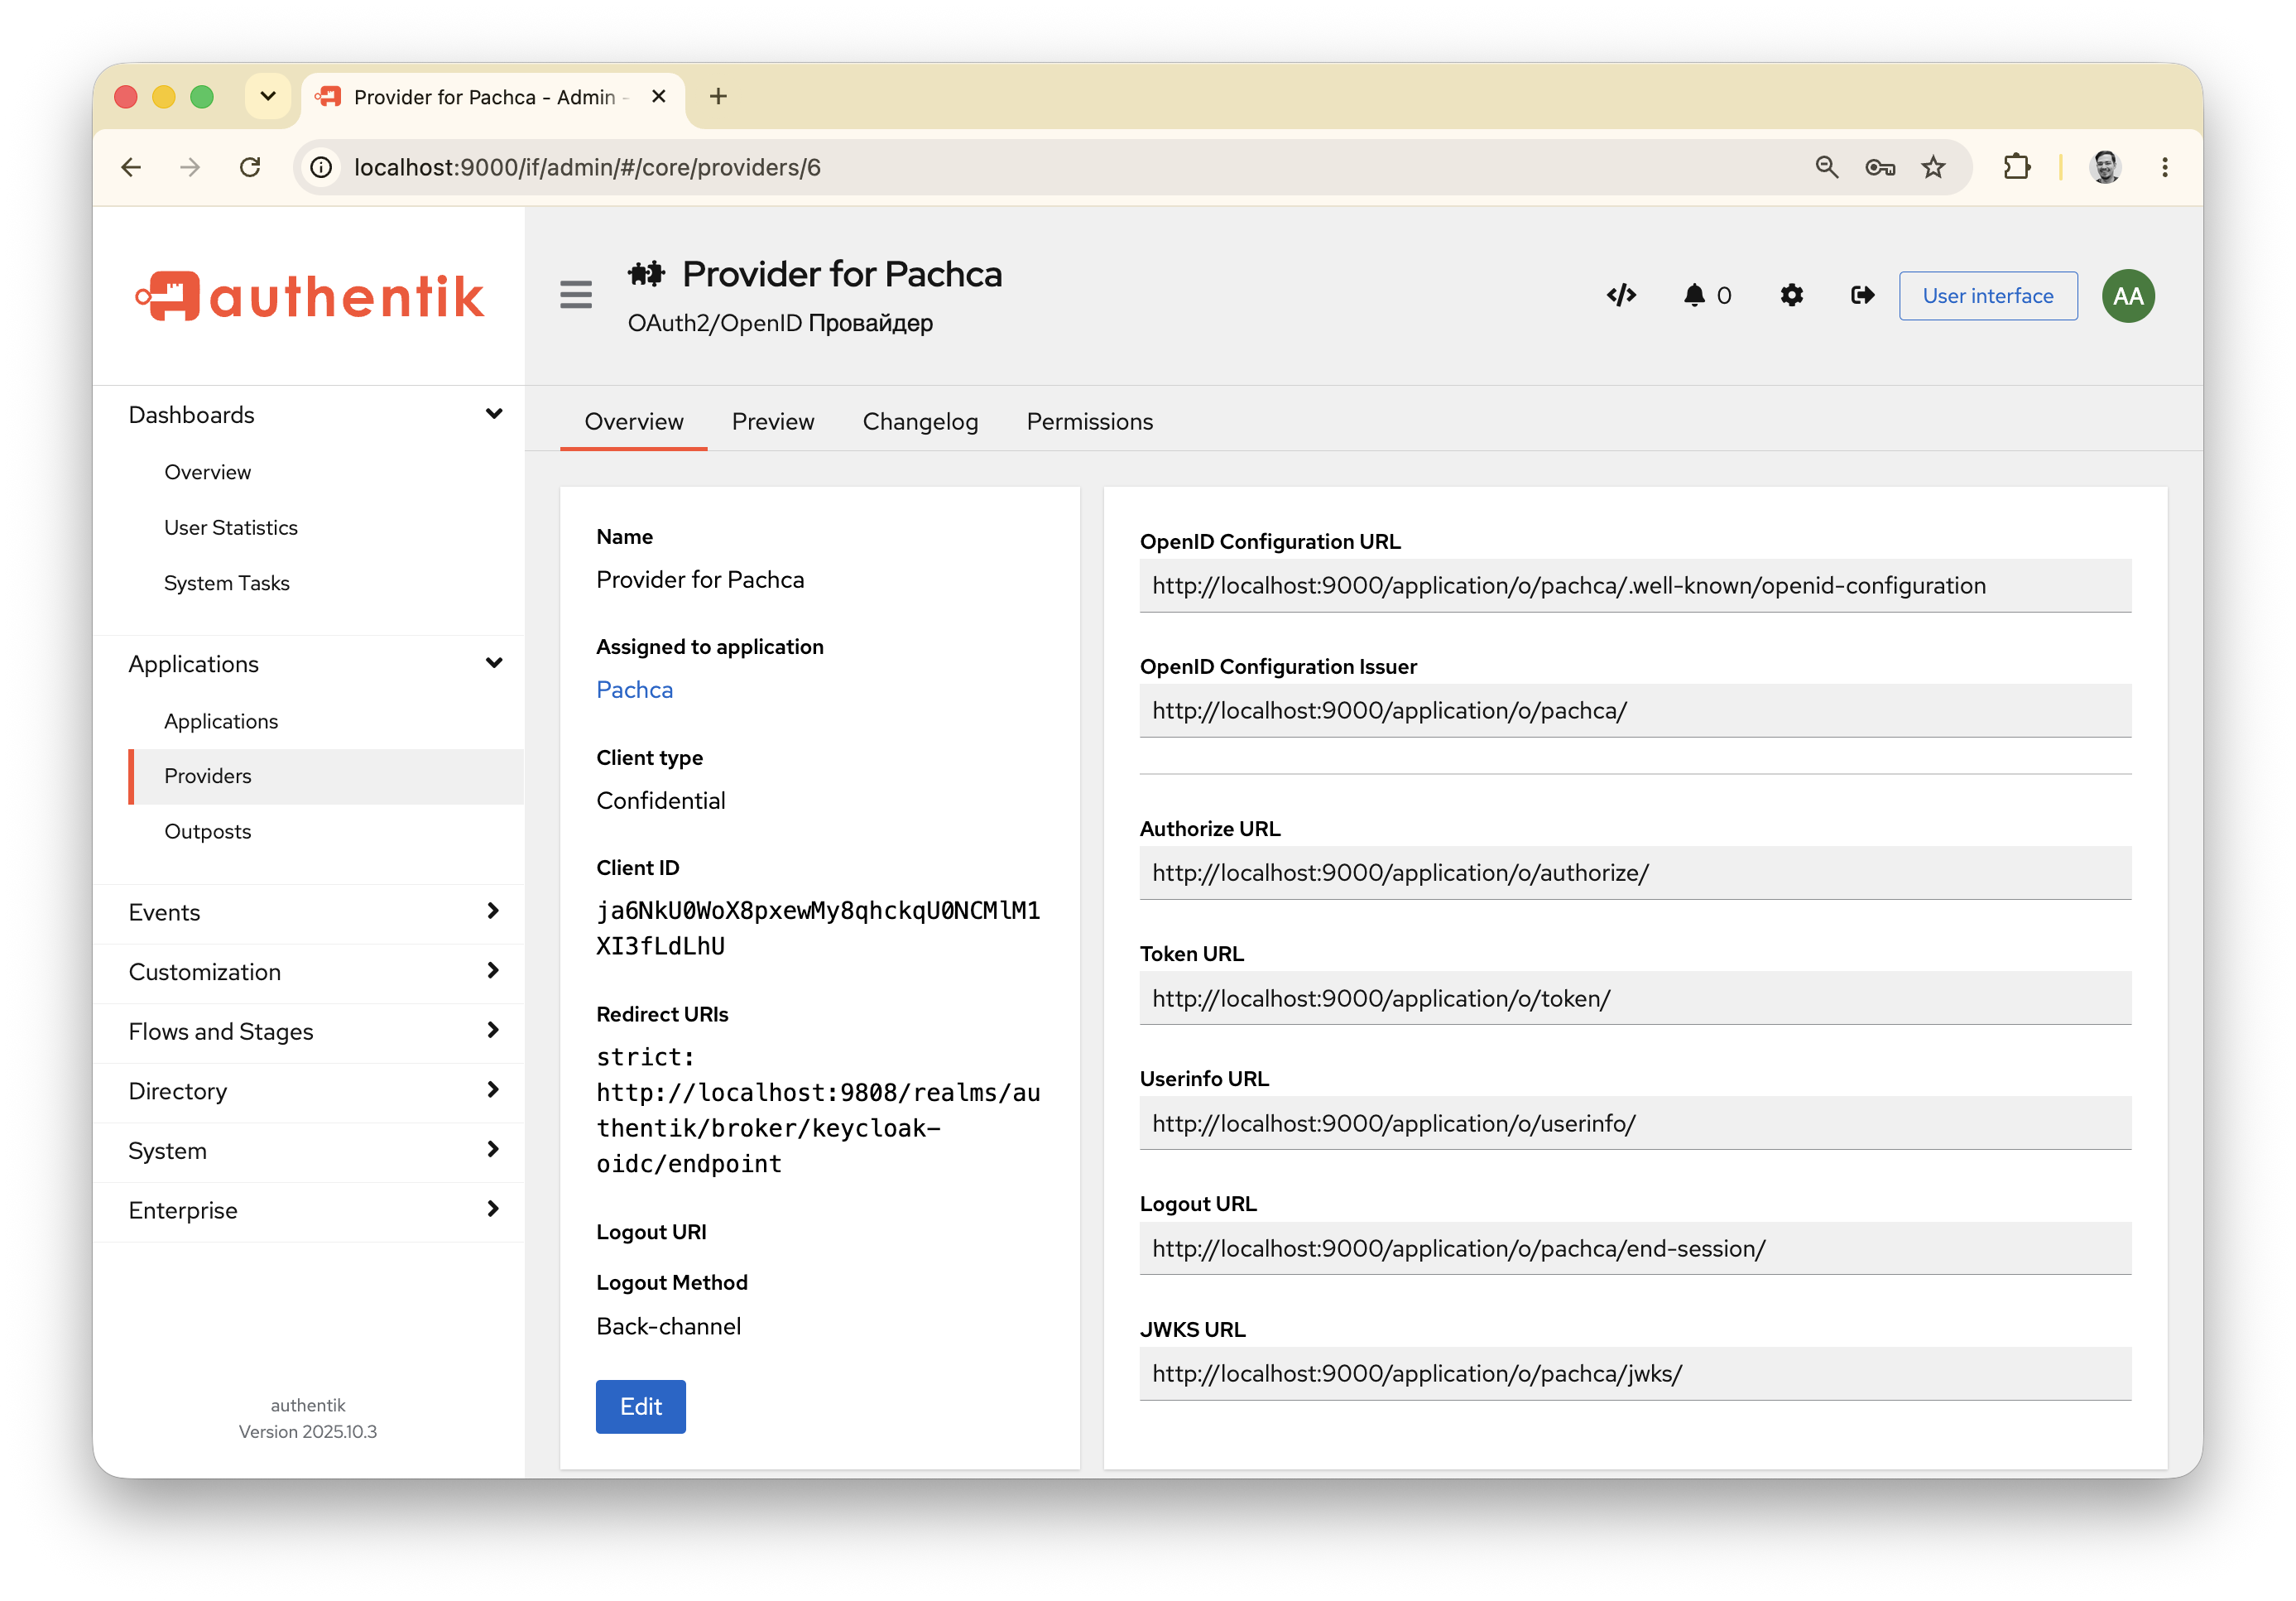
That's it for the configuration.
Send us the following details:
- OpenID Configuration URL
- Client ID
- Client Secret
Once we finish the setup on our side, you can log in to Pachca with SSO.
Updated: July 23, 2026